What is Cyber Due Diligence for M&A?
Cyber due diligence for M&A: a practical guide to cyber due diligence — what it covers, who it’s for, how it compares to market alternatives and how it fits into an M&A deal.
First report on your real target, free with 24h qualification. After that, standard pricing at €390 per dossier (10-pack for €3,200).
What is cyber due diligence?
A specific layer of the due diligence process focused on the target’s cyber risk: exposed attack surface, historical breaches, technical posture and key-personnel exposure. Outside-in, with no access to the internal network.
Fast
Full report in under 5 minutes, within the same investment committee session.
Auditable
Documented methodology and RFC 3161 timestamp. Defensible before the committee and the buyer.
Actionable
10 KRIs with clear severity and prioritized recommendations to negotiate price or W&I cover.
Who it’s for
Built for the players who need to resolve cyber risk on time without slowing down the deal calendar.
PE funds
Pre-close Cyber DD and portfolio monitoring.
Venture Capital
Screening startups in early-stage rounds.
M&A boutiques
Supporting sell-side and buy-side advisory.
Law firms
Technical annex for SPA and W&I.
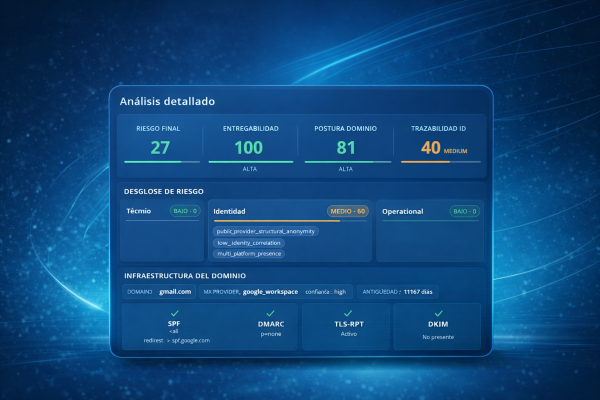
10 KRIs covered in the Cyber DD report
Each report analyzes 10 key cyber-risk indicators, grouped into actionable blocks with severity and a prioritized recommendation.
How it works
From request to delivery in under one session.
Review the sample
Download a real anonymized report to check the format and depth before committing budget.
Order the report
Provide the target (primary domain) and receive the automatically generated report with an RFC 3161 timestamp.
Decide in the session
10 KRIs with severity, findings and recommendations. Ready to attach to the SPA or support W&I cover.
Cyber DD vs. market alternatives
An honest comparison: when Cyber DD is the right fit, and when it isn’t, against the main players in the market.
| Solution | Delivery time | Cost per report | Model |
|---|---|---|---|
| IntelMind Cyber DD | < 5 minutes | €390 | Outside-in, automated, attachable |
| Big4 / cyber DD consultancies | 2 – 6 weeks | €30k – €300k | Inside-out with a dedicated team |
| BitSight / SecurityScorecard | Annual subscription | €20k – €80k / year | Continuous portfolio rating |
| Offensive pentest | 1 – 4 weeks | €8k – €60k | Audit with explicit authorization |
Cyber DD does not replace a deep audit with internal network access. It solves the first step: resolving cyber risk pre-LOI or pre-close within a reasonable budget and timeframe.
Frequently asked questions
What investment teams ask most before ordering.
Is the report legally valid as an SPA annex?
How long does it actually take?
How much does a report cost?
What exactly do the 10 KRIs cover?
Do I need to sign an annual contract?
How is this different from IntelMind’s OSINT SaaS tools?
Shall we start with a sample?
Download a real (anonymized) report in under 30 seconds, or book a demo with the sales team.
About cyber due diligence for M&A
These are the legal frameworks, institutions and authority references behind the professional use of cyber due diligence for M&A with IntelMind: